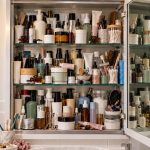
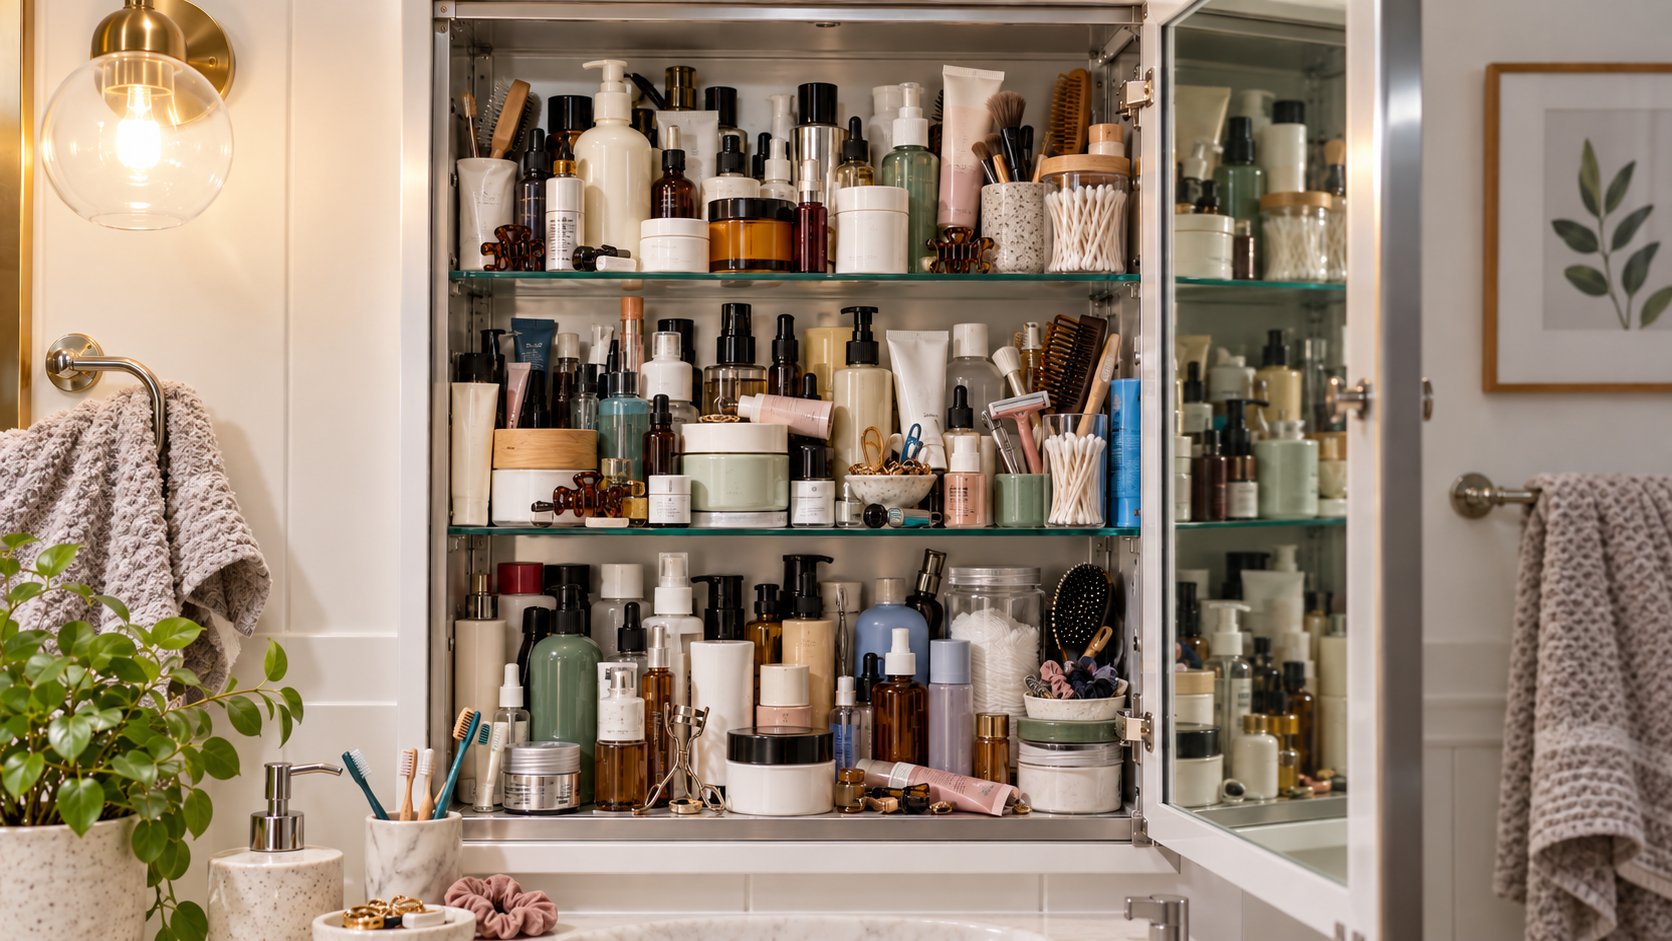
Open the cabinet above any bathroom sink in October and you will find the archaeology of every cold since 2021. Two kinds of decongestant. A bottle of vitamins nobody finishes. Something prescribed for a trip that is now three trips ago.
Nobody looks at that shelf and concludes the family is healthy. The shelf is a record of purchases, and that is all it is.
Alex manages a nine provider healthcare practice in Eugene, and her security setup looks a lot like that cabinet.
A ransomware scare three years ago prompted one purchase. The cyber insurance renewal required two more. A vendor recommended a fourth. Each decision made sense on its own.
Today she has seven security products, three of which do roughly the same thing, and no clear answer to the only question that matters: is the practice actually protected?
The myth that more tools means more security
It is an easy assumption. If one product adds protection, five should add more.
Layers are valuable when each one has a job. Trouble starts when products get added without anyone asking how they fit together.
Two tools that overlap create noise. Two tools that leave a gap between them create a false sense of coverage. Either way, the invoice goes up and the protection does not.
Do more security tools mean better cybersecurity?
Not by themselves. Security improves when the right safeguards are in place, someone is managing them, and they work together against the risks your business actually faces. A well run set of four tools beats a neglected set of nine every time, and it usually costs less.
Healthy security works like a system
Your immune system is not a shelf of remedies. It is a coordinated response that recognizes a problem, reacts to it, and remembers it for next time.
Business security should work the same way, but for most companies the pieces never got introduced to each other.
Tools were bought to solve specific problems. Policies were handed out. Training happened once. New safeguards arrived as requirements changed. Over time, each piece drifted away from the bigger picture.
Coordination is the missing ingredient. Safeguards should complement each other rather than coexist. Employees should know what is expected of them. And there should be a clear process for what happens when something suspicious shows up, because a tool that raises an alert nobody reads has not protected anything.
Who should be watching security alerts in a small business?
Someone with the time and the training to act on them, which in a 10 to 250 employee company is almost never an internal person with another full time job. An alert is only useful if a human reviews it and knows the next step. If the honest answer at your company is "the software handles it," that is a gap, not a plan.
Give your security a checkup
You do not need to understand the technical details of every product your company runs. You should be able to get a clear answer to four questions.
1. What did we buy, and what problem was it for?
Whoever runs your IT should be able to name each major product, say what it protects, and say why it was added. A shrug on any line item is your starting point.
2. Which tools are doing the same job, and what is nobody covering?
Duplication is fine when it was chosen. Two layers on email filtering can be a deliberate decision. The question is whether anyone made that decision or whether the second layer arrived with an insurance renewal and stayed.
How does a business owner know if security tools overlap?
Ask your provider for a one page map: each tool, the job it does, and the risk it covers. Two tools on the same line with no stated reason is duplication. A risk with nothing beside it is a hole. Most owners have never seen this map, and most providers can produce it in an afternoon if asked.
3. Whose name is on the outcome?
Software will happily generate alerts all night. Somebody has to own what happens next, and that person needs the time and the training to act. Without a name attached to the outcome, you own a dashboard, not a defense.
4. Does the setup still match the company we are today?
Companies drift. Staff turn over, a new line of business application shows up, half the office starts working from home, a credit union opens a branch in Bend. Protection that was sized for the 2023 version of your business may have nothing to say about the 2026 version.
How often should a business review its cybersecurity setup?
Once a year at minimum, and after any major change: a move, an acquisition, a new line of business software, a shift to remote work, or a change in compliance requirements. The review does not have to be long. It has to be honest, and it has to answer the four questions above with something better than "I think so."
A clearer view
10D Tech provides managed IT services and cybersecurity for businesses with 10 to 250 employees across Oregon and southwest Washington, from Portland and Salem through Albany, Corvallis, and Eugene to Bend.
The owners we meet who are exposed did not get there by being cheap. Most of them spent plenty. They got there because every purchase was made in isolation and nobody ever stood back far enough to see the shelf as a whole, which is nearly impossible from inside the building.
The job is to inventory what is running, name the duplicates, name the holes, and decide whether the whole thing still fits how the practice works today. Alex came out the other side with five products instead of seven and, for the first time, a yes she could defend. That is the usual ending.
What does a managed IT provider do about security tool sprawl?
The useful ones start by turning the shelf into a map: every product, the job it does, the risk it covers, and who is watching it. Then they consolidate where two tools do one job, close the holes nobody was covering, and take ownership of the alerts so a human is accountable for the outcome. What you get back is fewer invoices, one point of responsibility, and a plain answer to the four questions above. If your current provider cannot answer them, that is the real finding.
If you want to know whether what you have is a system or a shelf, we can tell you in fifteen minutes. A complimentary 15 minute Technology Confidence Score call gives you a clear picture of where your systems stand today, along with your score out of 100. See how the Score works at 10dtech.com/aspirin, then schedule at 10dtech.com/Tech_Confidence_Score. Albany, Corvallis, Eugene, Bend: 541-243-4103. Portland, Salem: 971-915-9103.